Amazon Virtual Private Cloud (VPC) Networking
A VPC is your own logically isolated private virtual data center inside AWS. It gives you complete control over your virtual networking environment, including IP address ranges, subnets, route tables, and…
Lesson 15 of 26 · Module: AWS
25 min read · Source notes — VPC Sizing & CIDR Block Security
A VPC is your own logically isolated private virtual data center inside AWS. It gives you complete control over your virtual networking environment, including IP address ranges, subnets, route tables, and network gateways.
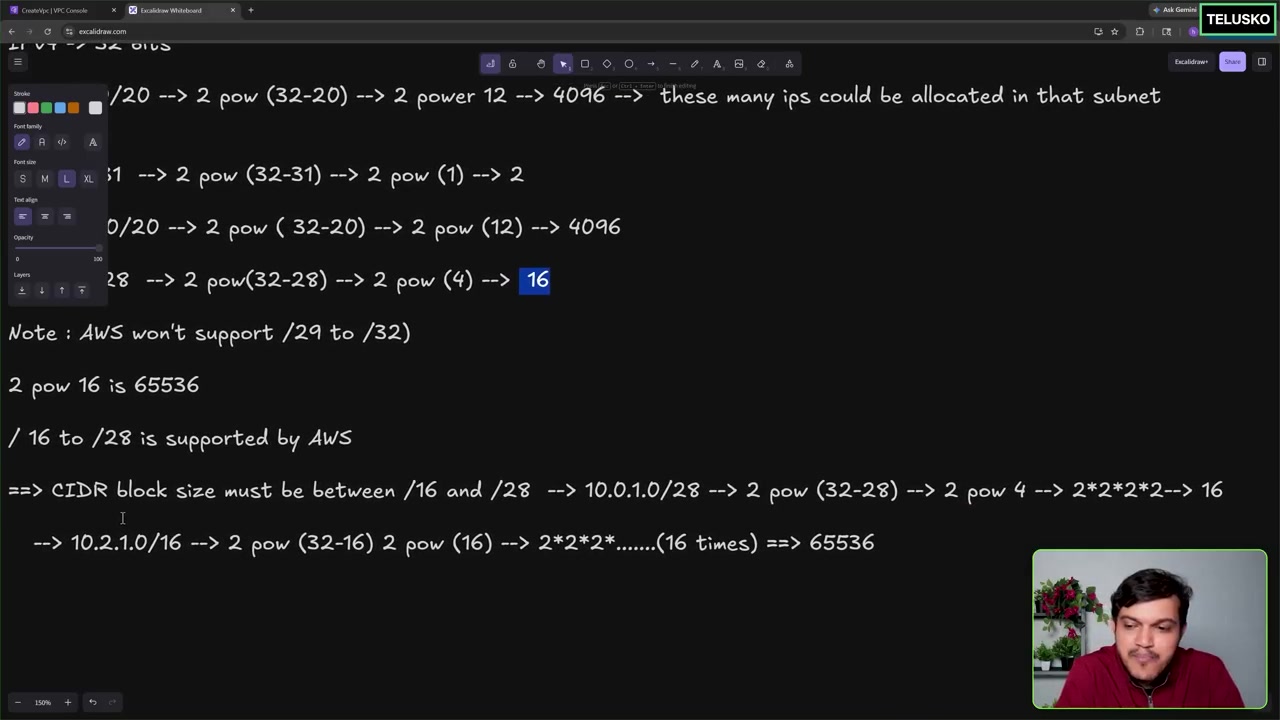
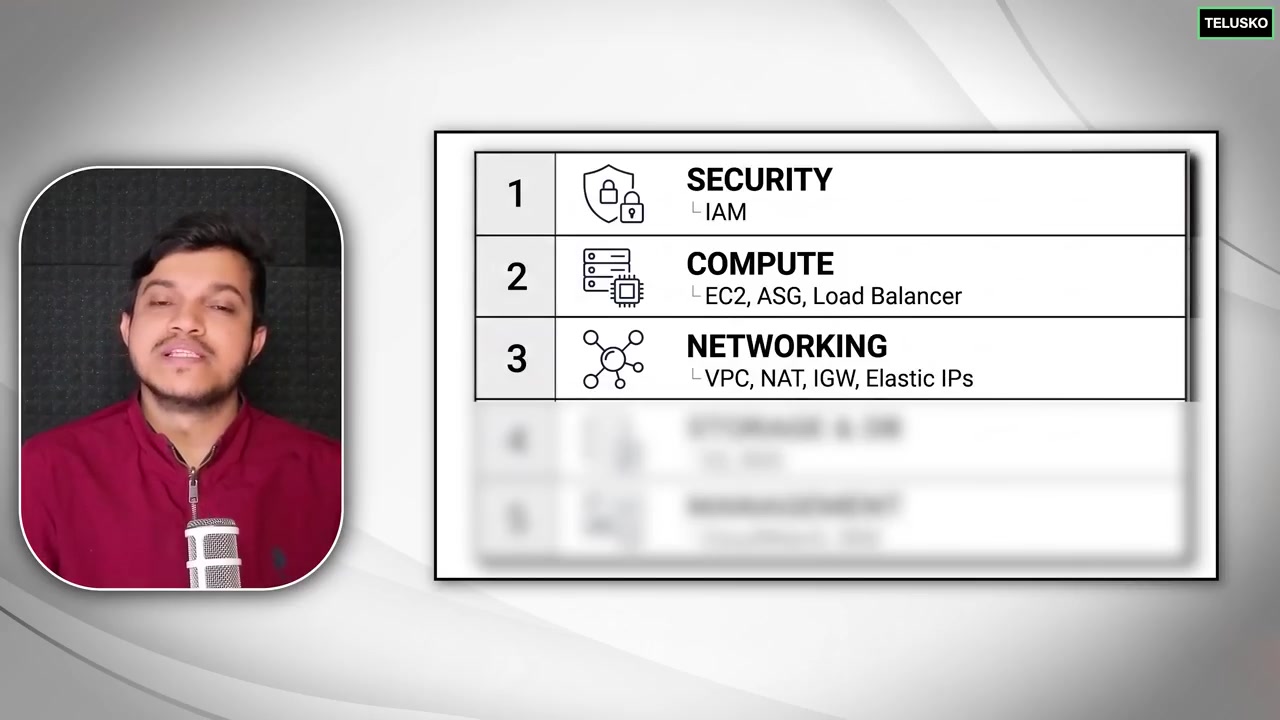
Instructor explaining CIDR prefix notation (/16 vs /24) and subnet partition math.
1. IPv4 CIDR Block Subnetting Math
AWS allows VPC sizes from /16 (65,536 IP addresses) down to /28 (16 IP addresses):
10.0.0.0/16: Standard enterprise VPC (IP range:10.0.0.0–10.0.255.255).- AWS Reserves 5 IP Addresses in Every Subnet!
10.0.1.0: Network address10.0.1.1: Reserved by AWS for VPC router10.0.1.2: Reserved by AWS for DNS server10.0.1.3: Reserved by AWS for future use10.0.1.255: Network broadcast address Therefore, a/24subnet (256 addresses) yields exactly 251 usable host IPs.
2. Public Subnet vs Private Subnet Architecture
| Subnet Type | Internet Gateway (IGW) Access | Workloads Placed Here |
|---|---|---|
| Public Subnet | Route Table points 0.0.0.0/0 directly to Internet Gateway (igw-xxxx). | Application Load Balancer (ALB), NAT Gateway, Bastion Jump Host. |
| Private Subnet | No direct route to IGW! Outbound internet flows through a NAT Gateway in the public subnet. | Backend application servers, microservices, databases (RDS, Aurora, DynamoDB). |
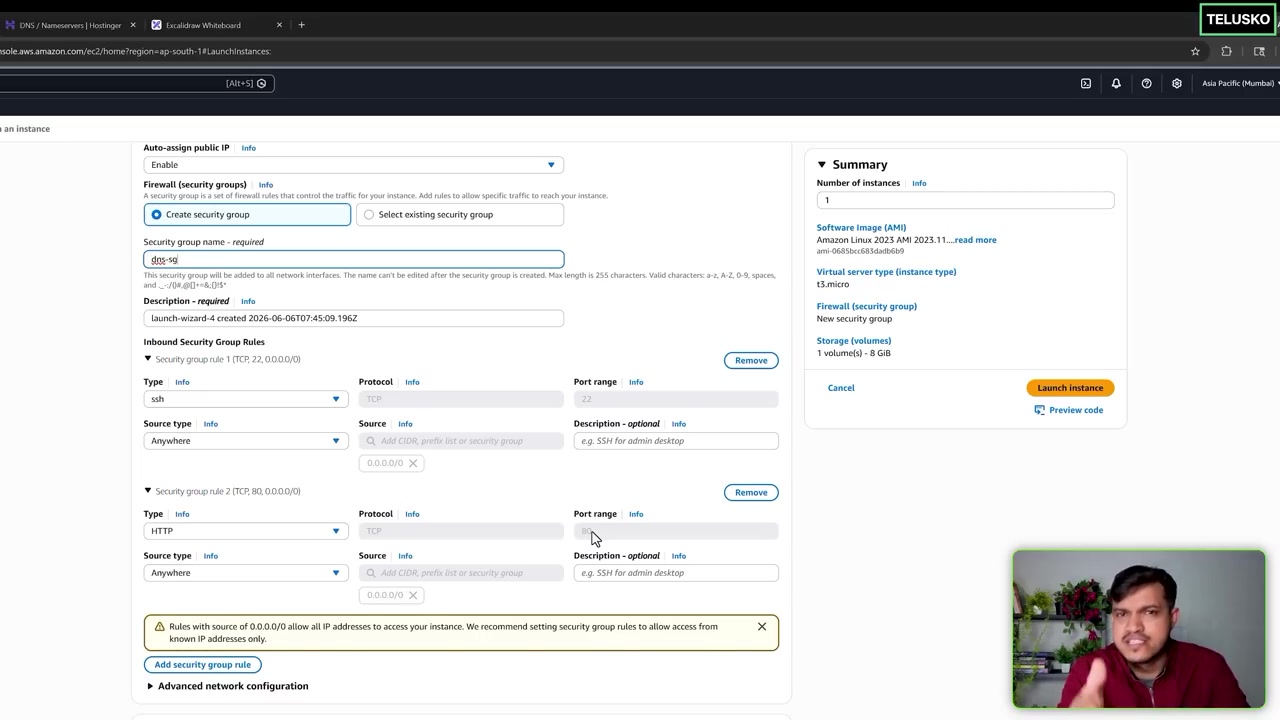
Mapping Route 53 DNS Alias A-records to the Application Load Balancer DNS name.
Keep going: ← Lesson 14 · Lesson 16 → · Module overview · Track it in the Self Guide
Finished this one?
Part of Self Guide · Stage 5: AWS fundamentals. Progress is saved in this browser.