W3DevOps Module · Coolify: A Sub-$10/Month PaaS, Step by Step
Why I run my own Heroku-style PaaS on a single GCP VM, how Coolify works under the hood (Docker + Traefik + SSH), and the five-step process for connecting extra servers — with the real screenshots.
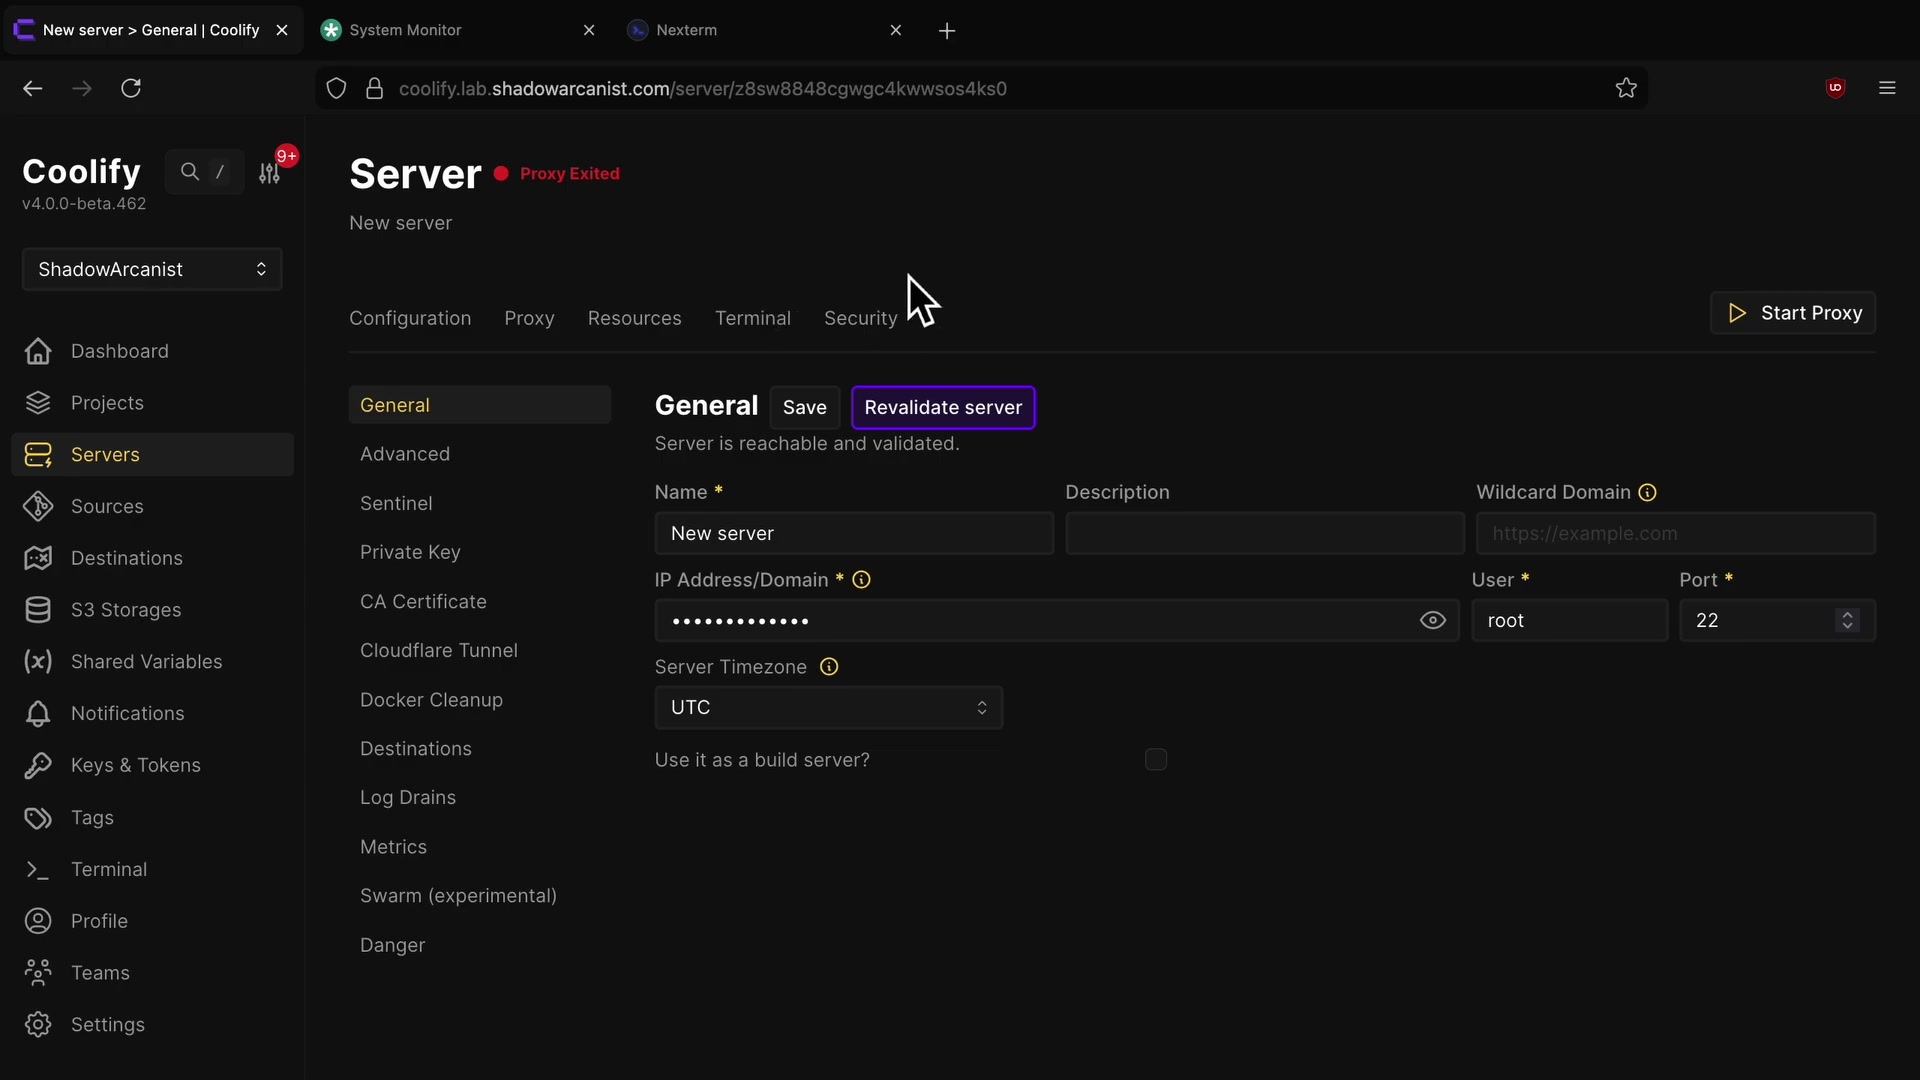
Managed container platforms are wonderful until you have ten small projects and each one wants its own monthly minimum. For my side projects and client previews I run Coolify v4 — an open-source, self-hosted alternative to Heroku/Netlify/Render — on a single Google Compute Engine instance in us-central1-b.
That gives me git-push deploys, automatic SSL, wildcard DNS and preview environments on a compute budget of under $10/month. The trade-off is that I'm the on-call engineer. This module covers Coolify, plus what I learned running it.
What this module covers
- What Coolify is and when self-hosting beats a managed PaaS
- How it works under the hood: SSH to each server, Docker Engine, Traefik
- Connecting a remote server in five steps: key →
authorized_keys→ register → validate → deploy
Lessons in this module
- Coolify: The Open-Source Self-Hosted PaaS — Coolify is an open-source, self-hosted Platform as a Service (PaaS) that brings the developer experience of Vercel, Heroku, and Netlify to your own hardware, VPS, or cloud instances. Instead of paying hefty…
- Connecting Remote Servers to Coolify (Step-by-Step) — By default, Coolify deploys applications onto the server where Coolify itself is installed. To scale horizontally, you can connect an unlimited number of remote cloud servers (AWS, Hetzner, DigitalOcean,…
Start with Lesson 24: Coolify: The Open-Source Self-Hosted PaaS — every lesson links to the next, and you can mark each one complete.
Running it for real
The decision. Managed AWS ECS/EKS would have been the "enterprise" answer. For a student with a dozen small apps, a single e2 VM running Coolify gives 90% of the developer experience at a fraction of the cost. The 10% I give up — multi-region failover, managed patching — I don't need for previews and portfolio demos. Anything that needs real uptime (Nora Labs, CryptoEdge) goes to Cloud Run instead.
What bit me
- Firewall first. GCP blocks everything by default. Coolify's dashboard (
:8000), HTTP/HTTPS (80/443) and SSH need explicit VPC firewall rules — the handbook has a whole lab on firewall rules for exactly this reason. - SSH permissions. Validation fails silently if
~/.sshisn't700andauthorized_keysisn't600. - Root is required. Coolify needs root on each managed server to install Docker and configure Traefik — so those servers should run nothing else.
- Keep the screenshots of failures. The handbook deliberately includes real SSH and permission errors, because that's what you'll actually see at 1 a.m.
That's the end of the handbook series. For how all of this comes together in CI/CD across my projects, read How I Ship 23 Projects.
Keep going: Start the module → · Full course outline · Self Guide
Finished this one?
Part of Self Guide · Stage 8: Self-hosting with Coolify. Progress is saved in this browser.